Identity
Defines the principal’s permitted access.
For the builders of agentic AI
Give enterprises the confidence to let agents do more. Maya adds independent, per-agent control on the network path. No traffic decryption. No agent code changes.
The missing layer
One agent in a fleet goes wrong. Can you identify it? Can you stop it?
Defines the principal’s permitted access.
Govern activity within the agent’s runtime.
Enforces the agent’s mandate on its connections.
An independent layer that complements model and runtime safeguards.
From intent to control
You set the policy. Maya applies it to every connection.
Define an agent’s policy mandate once, centrally.
Discover agents and attribute each connection to the agent that made it.
Expose undeclared agents and traffic that deviates from a mandate.
Evaluate the observed behavior against the policy you defined.
Allow, limit or stop the agent or the specific flow. Reversibly.
Illustrative connection policy
An independent control layer
The agent can act. The enterprise sets the boundaries.
Maya runs in your own cloud account and VPC.
Payload-blind enforcement. Maya never decrypts traffic.
Zero changes to agent code.
Enforcement is scoped to the agent, or to flows within its traffic.
One governed fleet
Available now on AWS and GCP, in your cloud account.
Where agents run
Remote workers, Linux servers, Kubernetes, cloud agent runtimes and container platforms.
Where they connect
LLM endpoints, databases, object storage, MCP servers and SaaS services.
How teams operate
Central policy and connection evidence, with OpenTelemetry export and gRPC and REST APIs. Works with Okta, SPIFFE and cloud IAM.
Team
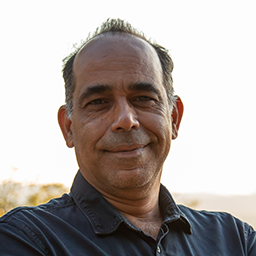
Founder & CEO
Networking datapath architect with nearly three decades building forwarding planes, deep packet inspection, QoS, and control-plane security at Cisco, Juniper, and Brocade, and cloud infrastructure at IBM and Oracle. He built Maya's eBPF datapath and agent-identity model. Nine US patents. M.S. Computer Engineering, Santa Clara University.

Co-founder & CTO
Founding engineer of Cisco's network infrastructure security group, where he worked on Control Plane Policing and deep packet inspection, then product and go-to-market leader at FireEye, Mandiant, SentinelOne, Cyberinc (acquired by Forcepoint), Elastic, and Anomali. Published IETF RFC author. MBA, UC Berkeley Haas.
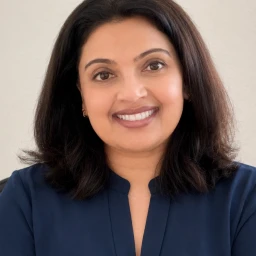
VP of Engineering
Engineering leader with 25 years in networking, cloud infrastructure, and security. Most recently Director of Software Engineering at Palo Alto Networks, leading a cloud platform processing 2 trillion events and 6 PB daily across 20+ countries. Her experience includes FedRAMP compliance. She leads Maya's engineering organization, including data plane, control plane, and multi-cloud deployment. US patent inventor. B.Tech, College of Engineering Trivandrum.
Build with us
Now onboarding model builders, agent platforms and research teams. Bring a workflow that matters to your customers, and we test how agent identity, policy and connection evidence hold up as autonomy grows.
Agree on the runtime, destinations and behavior to evaluate.
Define a mandate, then test undeclared agents and connections beyond it.
Assess agent attribution, enforcement and the effect on the rest of the fleet.
Let’s start a conversation
Or email partner@mayagentic.com to explore a partnership. Research inquiries: research@mayagentic.com.
Free · two weeks · your environment
See which agents are operating, where they run, and what they communicate with.
Cookies
We use analytics cookies to see how this site is used so we can make it better. Decline and we switch them off. See our privacy policy.